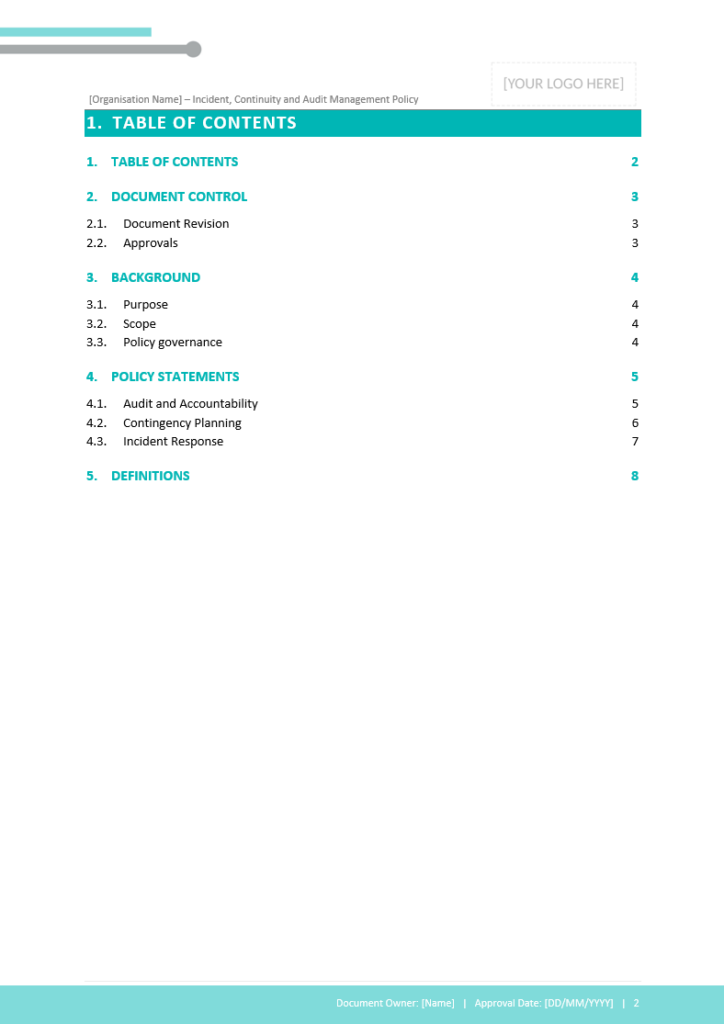
This policy establishes the requirements for managing security incidents, maintaining business continuity, and conducting audits to ensure organisational resilience, regulatory compliance, and the ongoing effectiveness of security and operational controls.
This policy provides a framework for detecting, responding to, and recovering from security incidents, maintaining the availability of crucial business functions during disruptions, protecting and monitoring audit logs, and ensuring effective recovery, accountability, and compliance activities to support organisational resilience. Aligned to the NIST Cybersecurity Framework (CSF) and informed by NIST SP 800-53 security controls, it helps organisations implement industry-recognised security governance practices.
Our policy templates are designed by experienced cybersecurity consultants to accelerate policy development and security program maturity.
Rather than starting from a blank page, you can leverage a professionally developed policy and tailor it to suit your organisation’s specific requirements, operating environment, and risk profile.
The policy is provided in Microsoft Word format. ready for customisation and implementation.
This policy is suitable for organisations seeking to establish or mature their cybersecurity governance framework and risk management practices, including:
The policy includes guidance on:
Pick the modules you need, download instantly, and own them for life—no subscriptions, no ongoing costs.
Drop the SCORM files into your existing LMS. Fast, seamless integration with most major platforms.
Engaging content your team will remember. Track completions and compliance with ease.
Click here to be redirected to our free video for you to download and test in your LMS.
Whether you’re wondering about how our modules work, how to integrate them with your LMS, or what’s included in each purchase, our FAQs below have you covered.
We are committed to staying current with cybersecurity trends and threats. Our content is regularly updated to reflect the latest developments, ensuring your team learns the most relevant information.
Absolutely. Our training modules are designed to cater to all levels of expertise. We use simple language and relatable scenarios to make the content accessible and valuable for both technical and non-technical staff.
Yes. All our modules are SCORM-compliant and designed for seamless integration with most learning management systems.
No problem! There are several free or cost-effective LMS options available that could work well for your training needs if you don’t have your own LMS. Open-source platforms like Google Classroom and Moodle are popular choices that many organisations use successfully for security awareness training. Microsoft Viva Learning may also be an option, depending on your current licencing.
Once you have a preferred LMS in place, our training modules integrate easily, and you will have a complete training solution.
A SCORM file (Sharable Content Object Reference Model) is a standardized package of eLearning content that can be uploaded into a Learning Management System (LMS). It allows for consistent delivery, tracking, and reporting of training modules across different platforms.
We use SCORM 1.2, the most widely supported version across LMS platforms.
Absolutely. Each product page includes a short preview video showcasing the module’s style, tone, and key content.
Our products are sent out in SCORM 1.2 format, which is compatible with most Learning Management Software. However, we have created a free video for you to download and test in your LMS which you can find in the shop under “LMS Test Video”.
We aim to meet core accessibility requirements, including captions, clear audio, and readable text. While not fully WCAG-certified, our modules are designed with inclusivity in mind.
Our modules cover core cyber security awareness topics, including phishing, social engineering, safe web browsing, data protection, password hygiene, and more. View our Shop for full training catalogue for details.
Absolutely! Our modules are designed for businesses of all sizes with no ongoing licensing fees or user limits – your costs stay predictable as you grow.
Whether you’re a small team or large enterprise, educated employees are your most effective security control.
Yes. All videos include closed captions to support accessibility and improve comprehension for all learners. Captions are embedded and meet common accessibility standards.
No. Once you purchase a module, you can deploy it to as many users as your LMS allows — no user limits or ongoing costs.